Modder cracks Xbox 360 open for a voltage glitch mod
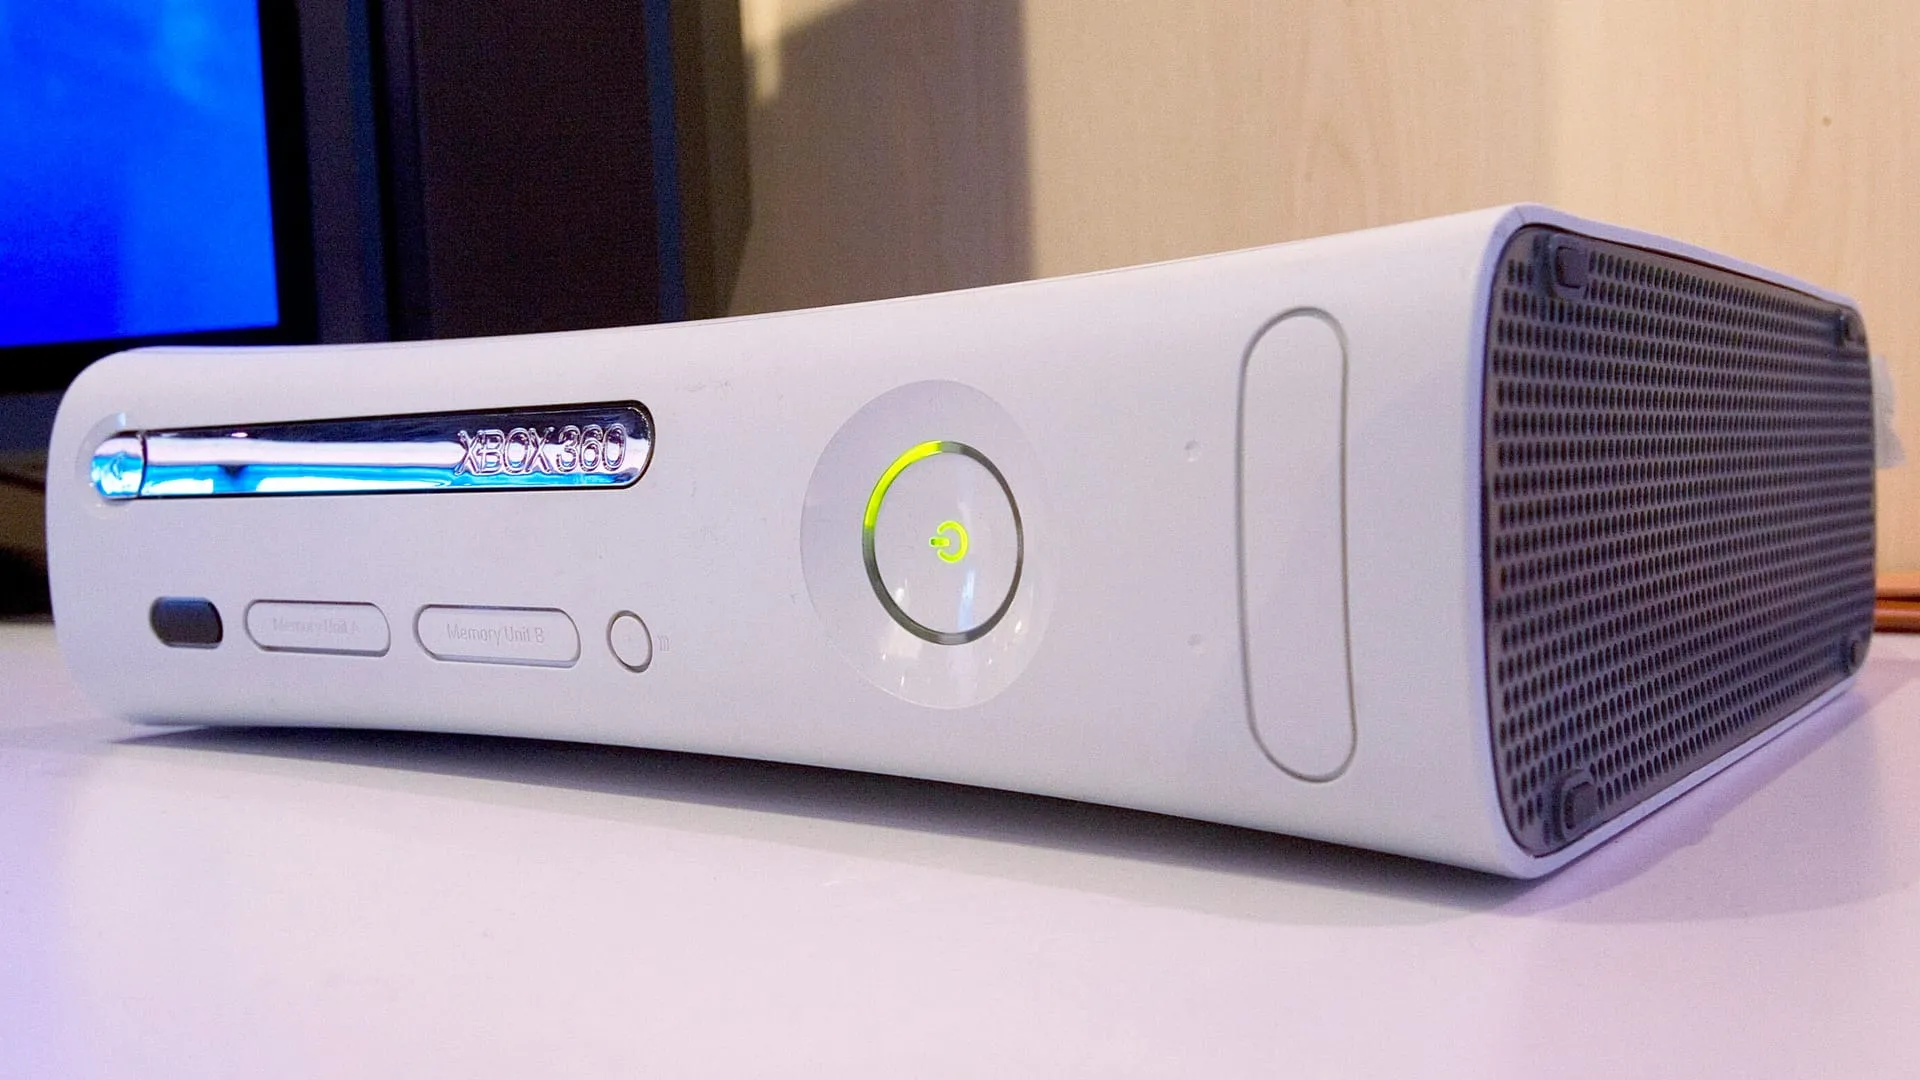
The journey of hacking gaming consoles is a fascinating blend of ingenuity and persistence. For years, enthusiasts have sought ways to push the limits of Microsoft’s impressive security architecture, peeling back layers of code to unlock new possibilities for the Xbox 360. The history of these exploits is a testament to a decade-long quest by modders to find the hidden signals and wires within the console’s system.
Early attempts involved complex methods, including modifying DVD firmware in 2006, implementing hypervisor hacks in 2007, and exposing JTAG debugging ports in 2009. The most enduring physical exploit, however, revolved around a CPU force-reset maneuver, which required specialized hardware and intricate timing.
This specific method involved sending a minute signal directly into the CPU’s reset pin. While the intent was simple—to trigger a reset—the result was far more disruptive. The CPU, instead of executing a clean reboot, executed the current instruction incorrectly. Successfully leveraging this flawed execution was the key to bypassing Microsoft’s sophisticated cryptographic layers.
Achieving this hack demanded spectacular precision. The process required timing down to the nanosecond, and often necessitated specialized glitch chips that required multiple attempts to achieve a successful “latch.” This level of detail made the process incredibly demanding for anyone attempting it.
Pioneering figures like Joshua Kennedy tackled this challenge in 2017. To perform the exploit, he relied on highly specialized components, requiring extensive soldering of wires, NAND chips, and programmers. It was a meticulous, time-consuming effort that required immense patience to bring the project to fruition.
Fast forward to 2026, and the landscape of console modification has been radically changed by accessible technology. The complexity of the operation was finally rendered trivial by the emergence of the Raspberry Pi Pico. This small, highly capable microcontroller-on-a-stick, priced affordably at just $4, offered a new pathway for high-level hardware manipulation.
By connecting the Pi Pico to the console’s interface, modders could now easily dump the console’s NAND flash firmware. Armed with this access, they could combine the timing files—mini-programs designed to trigger the glitch chip at the exact critical moment—with the new microcontroller. This shift transformed a multi-year, highly technical endeavor into a straightforward process.
The result was remarkable: a hack that once required specialized, expensive hardware and painstaking labor was made trivial by a budget-friendly chip. The ingenuity of the modders, combined with the democratization of microcontrollers, has fundamentally reshaped how hardware security is approached in the world of console gaming.
Buy on Amazon
Credit
