AI exploits Siemens controllers in critical infrastructure
The Invisible Threat: How AI and Hackers Are Targeting Critical Infrastructure
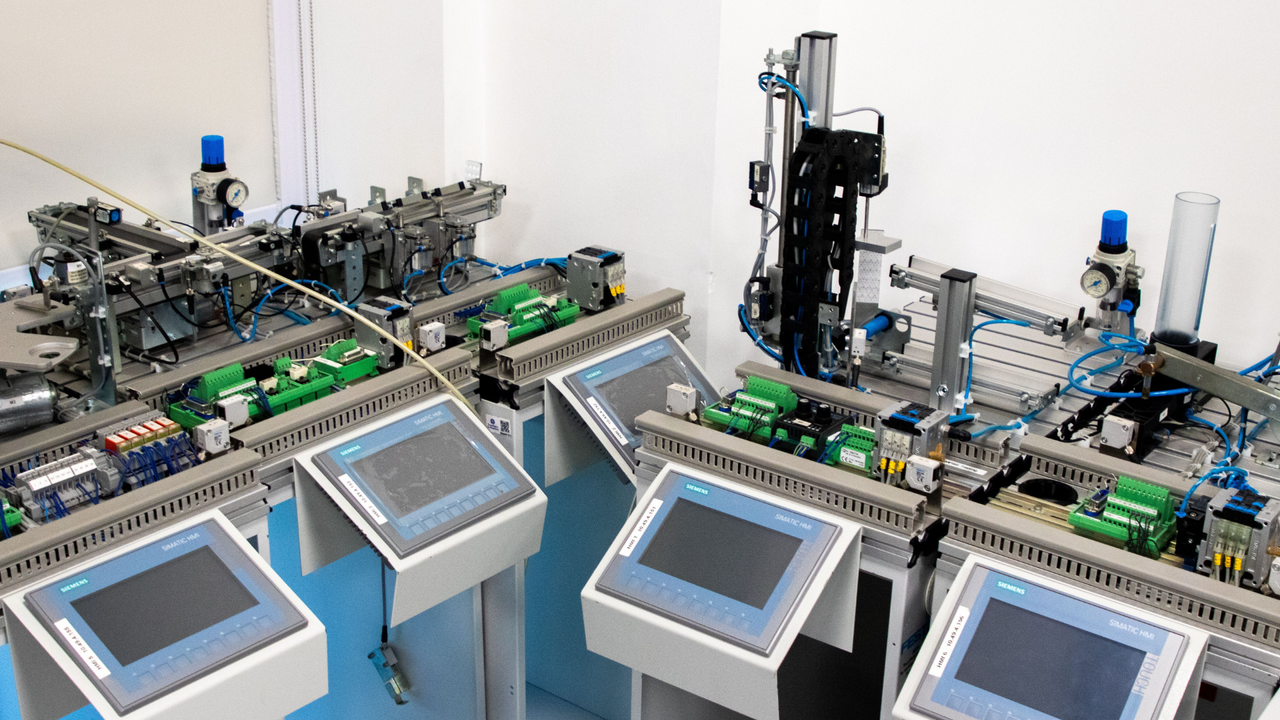
A growing chorus of U.S. government agencies has issued a stark warning regarding a sophisticated cyber threat targeting the backbone of critical infrastructure: Siemens S7-series programmable logic controllers (PLCs).
This isn’t just abstract digital risk; it is an active, tangible threat leveraging publicly available data to unlock the control systems that manage our essential services. Hackers are using these widely deployed devices to develop exploits that allow them remote access and control over industrial operations.
The danger escalates further through the integration of artificial intelligence. Attackers are now deploying AI tools not only to scan for vulnerable, Internet-exposed PLCs running outdated software but also to anticipate defensive measures, allowing them to adapt their malicious files to mimic legitimate monitoring tools. This technological evolution makes the threat exponentially more difficult to defend against.
The scope of this vulnerability stretches across virtually every sector of the economy. The agencies have flagged Critical Manufacturing, Energy, Water and Wastewater, Chemical, Food and Agriculture, and Commercial Facilities as the most likely targets. Exploiting these poorly protected industrial control systems (ICS) could lead to catastrophic consequences, including the disruption of critical processes, safety incidents, equipment damage, and cascading failures across interconnected systems.
The coordinated warning, issued by organizations including the Cybersecurity and Infrastructure Security Agency (CISA), the National Security Agency (NSA), the Federal Bureau of Investigation (FBI), the Department of Energy (DOE), and the Environmental Protection Agency (EPA), underscores the severity of the situation. This is not a theoretical risk; it is an active threat demanding immediate attention from system operators.
The intersection of cyber warfare and physical infrastructure has become increasingly apparent. Past events have shown how cyberattacks can be used in conflicts, inflicting damage while maintaining plausible deniability, whether in active warfare or through less overt forms of conflict. The proliferation of internet-connected devices has made critical infrastructure an irresistible target for both financial gain and geopolitical advantage.
To safeguard these essential systems, operators using Siemens S7 PLCs and other critical infrastructure devices are advised to implement robust defensive strategies immediately. Key steps include ensuring all equipment receives the latest security patches, isolating these systems from the public internet whenever possible, enforcing strong access controls, and deploying advanced monitoring tools to detect any anomalies in industrial control systems.
By treating industrial control systems with the same rigor as national security operations, operators can mitigate this sophisticated threat and ensure the resilience of the critical services that underpin modern society.
Credit