AliExpress fingerprints your PC using hidden audio code
The Secret Soundtrack: How a Tech Giant Was Caught in an Audio Fingerprinting Web Hunt
In the high-stakes world of digital privacy, some of the most insidious data collection methods operate beneath the surface of our screens. A recent investigation into the operations of a multinational tech giant revealed that hidden audio processes within global online marketplaces were being used for sophisticated audio fingerprinting—a method that could allow companies to track users without explicit consent.
The discovery began with a simple quest for audio fidelity. A developer testing wireless headphones found that browsing certain webpages, specifically those on the AliExpress platform, disrupted multipoint Bluetooth audio features. While the immediate fix was closing the tab, the real investigation unearthed something far more complex lurking within the browser’s audio architecture.
The investigation quickly moved beyond simple media testing. Researchers discovered that the problem wasn’t immediate, but rather occurred after the webpage sat idle for a few seconds, pointing to a deliberate, stealth mechanism. By examining the Web Audio API, the team wrapped critical functions to record every instance where a page created an audio-processing context and monitored what was connected to the audio destination.
Deep within the code, two suspicious scripts, collina.js and fireyejs.js, were uncovered. These scripts were not there for aesthetic reasons; they were actively engaged in a subtle form of digital espionage. Using a sawtooth oscillator to generate a waveform, the scripts created a complex Web Audio graph. An analyzer measured the results as the audio passed through the browser’s system, while a second script simultaneously read the resulting frequency data.
Crucially, these scripts operated silently. They set the volume gain to zero, ensuring no audible sound or noise was generated. Yet, while remaining silent, the browser continued to perform live audio processing, keeping the Bluetooth audio path active and preventing seamless switching between multiple devices. This continuous, passive processing was the core mechanism for data capture.
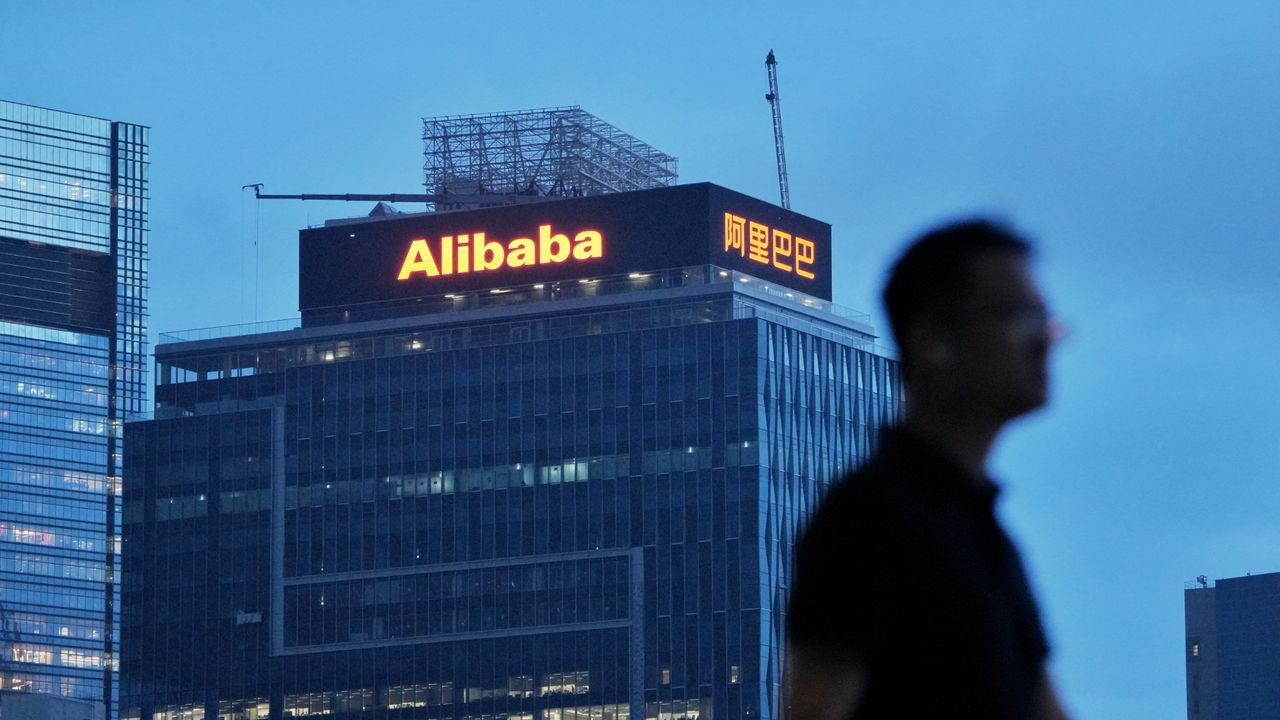
Beyond the audio, the investigation revealed a massive trove of personal information being harvested. The code was collecting granular details about the user’s environment, including screen dimensions, device memory usage, browser plugins, WebGL rendering capabilities, supported audio and video formats, mouse events, and much more. This rich dataset was then serialized and encrypted before being transmitted to Alibaba’s telemetry services via standard functions like fetch() or sendBeacon().
This exposure prompted immediate action from the browser community. Firefox, for instance, has introduced robust built-in protections against this kind of fingerprinting. Firefox 118, released in September 2023, included specific safeguards targeting Web Audio-based tracking, demonstrating a shift toward prioritizing user privacy within the browser framework.
Similarly, other browser makers are responding to the threat. Brave, for example, aims to block audio fingerprinting by default. Their approach involves injecting randomized data into the browser’s audio output, ensuring that the generated fingerprint appears unique to every session, effectively disrupting the ability of trackers to build persistent user profiles.
Buy on Amazon
Credit